We have officially kicked off our compliance journey with the team at Sprinto, taking a further step in strengthening how we protect customer data and manage information security.
For us, this work connects directly to what we do every day. We help organisations build and maintain HubSpot environments, connect business systems and make their data more useful. That comes with a responsibility to handle information carefully and to be clear about the processes supporting that work.
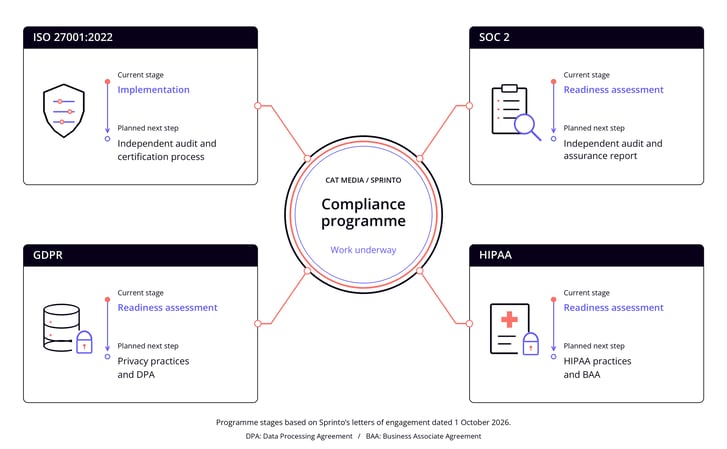
Our programme with Sprinto covers ISO/IEC 27001:2022, SOC 2, GDPR and HIPAA. The work includes implementing our information security management system, assessing readiness across the other programmes and preparing for the independent assessments and privacy arrangements set out in our engagements.
We wanted to share what this work involves, why it matters to our customers and how each area supports our approach to information security and privacy.
Why this matters for connected CRM and data
A CRM rarely works in isolation. Customer information can move between websites, sales and service teams, reporting tools and connected platforms. Every connection raises practical questions about access, purpose and responsibility.
Who needs to see a particular record? What information should an integration transfer? How long should data be kept? What happens when someone's role changes or a supplier introduces a new service?
These decisions affect how a system operates and how confidently an organisation can use it. They also explain why security and privacy need attention throughout a project, from the first architecture discussion to ongoing administration. At Cat Media, our compliance programme supports that approach by bringing more structure to the policies, risk management and evidence behind our own operations.
What we have put in place so far
Our initial onboarding milestones with Sprinto cover:
-
Policy setup
-
Risk register setup
-
Vendor risk register setup
These foundations help us document expectations, identify risks and review the suppliers involved in delivering our services. They give the team a clearer way to assign responsibility and track the work that needs attention. Sprinto's letters of engagement, dated 1 October 2026, set out the next stages in more detail.
Our ISO 27001 engagement is in implementation, while SOC 2, GDPR and HIPAA are in readiness assessment. The programme is underway. ISO 27001 leads towards an independent audit and certification process, while SOC 2 leads towards an independent audit and assurance report. The GDPR and HIPAA engagements focus on the relevant privacy practices and contractual arrangements. These are different outcomes, so we want to be clear about what each part of the work involves.
The areas covered by our compliance programme
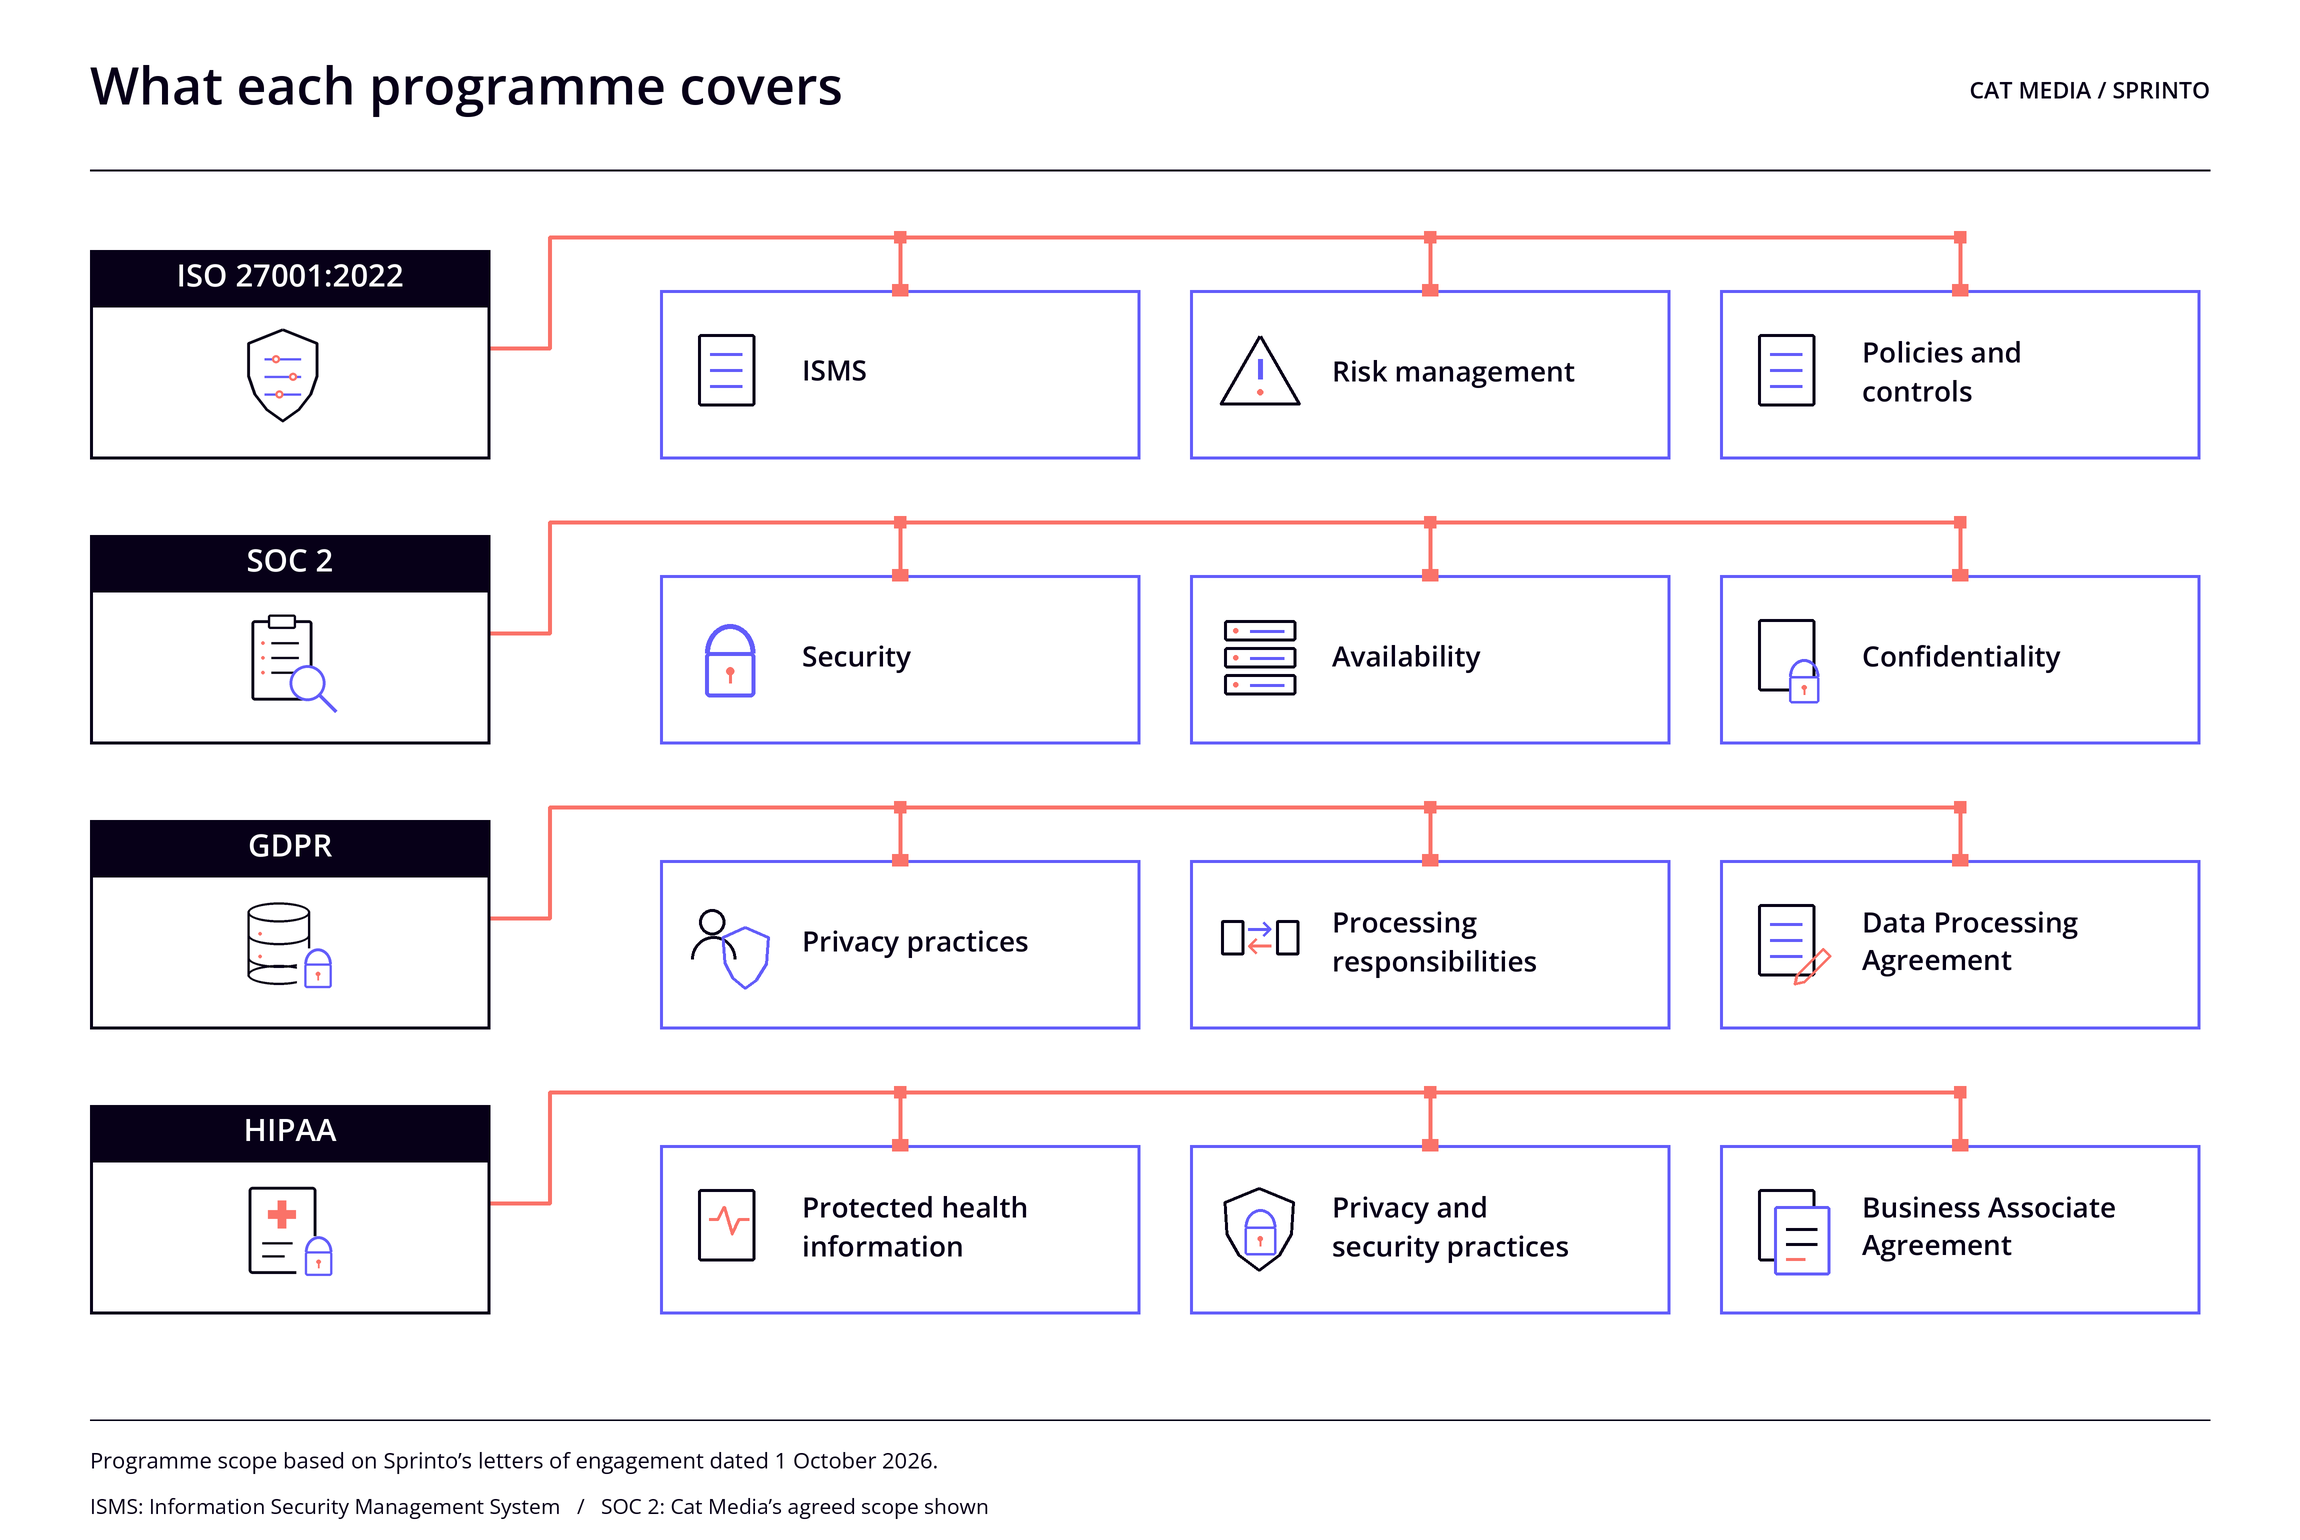
Our programme brings together information security management, data protection, independent assurance and the requirements around protected health information. Each area addresses different responsibilities, with shared foundations in how we manage risk, document our processes and protect data.
ISO 27001 provides a structure for managing information security
ISO/IEC 27001:2022 is an international standard for information security management systems, often shortened to ISMS.
In practical terms, an ISMS gives an organisation a structured way to understand its information security risks, put appropriate controls in place and review how well those controls work. It covers people and processes alongside technology.
The aim is to protect the confidentiality, integrity and availability of information. That means managing who can access it, protecting it against inappropriate changes or loss and keeping it available when needed. Sprinto is helping us implement this management system within Cat Media. The engagement then provides for an independent ISO 27001 audit and certification process. Certification will depend on that assessment; our current work is the implementation needed to prepare for it.
GDPR keeps the focus on people and their personal data
The General Data Protection Regulation sets legal requirements for handling personal data. Those responsibilities already apply where relevant; a readiness programme helps an organisation assess and document how it meets them.
Ireland's Data Protection Commission explains the core data protection principles, including fairness and transparency, collecting only what is needed, maintaining accuracy, limiting retention and protecting information appropriately. Organisations must also be able to demonstrate their compliance.
For CRM projects, that connects to everyday choices about forms, access permissions, data quality and retention. Processing also needs an appropriate lawful basis; consent is one possible basis, rather than the answer to every situation.
Our GDPR engagement is currently in readiness assessment. It sets out a path towards implementing the relevant privacy practices and having a Data Processing Agreement (DPA) in place as part of the planned outcome.
A Data Processing Agreement documents the responsibilities that apply when personal data is processed on a customer's behalf, including the scope of processing and the relevant obligations. This contractual work supports accountability alongside the operational privacy measures. GDPR obligations continue to apply throughout the programme.
SOC 2 helps customers assess a service provider's controls
SOC 2 is an assurance reporting framework developed by the American Institute of Certified Public Accountants. An independent CPA firm examines controls within a defined scope against relevant Trust Services Criteria.
Our SOC 2 engagement specifically covers the Trust Services Criteria relevant to Security, Availability and Confidentiality. This focuses the programme on protecting systems against unauthorised access, supporting their availability for use and safeguarding information designated as confidential.
The outcome of a SOC 2 examination is an assurance report, rather than an ISO-style certification. The report describes the defined scope and the auditor's findings about the controls examined.
We are currently in the readiness assessment phase for SOC 2. The engagement provides for an audit by an independent CPA audit firm after that phase. Our preparation focuses on the controls and supporting evidence needed for that examination, giving customers a clearer basis for assessing our services when a report becomes available.
HIPAA addresses specific responsibilities around US health information
The Health Insurance Portability and Accountability Act is US legislation. Its rules apply to specified healthcare organisations, known as covered entities, and their business associates.
HIPAA includes requirements around protected health information. Its Security Rule addresses administrative, physical and technical safeguards for electronic protected health information.
Our HIPAA engagement with Sprinto is in readiness assessment. The planned outcome includes implementing the relevant HIPAA practices and having a Business Associate Agreement (BAA) in place to support applicable customer engagements.
A Business Associate Agreement sets out responsibilities around the permitted use, disclosure and protection of health information in a business associate relationship. It is an important contractual part of the work, alongside the safeguards and operational practices required for the services involved.
For healthcare CRM and integration projects, the requirements still need to be established around the organisation's role, the information involved and the services being provided. Our HIPAA programme supports that preparation; the right data handling, configuration and agreements remain essential for each applicable engagement.
How Sprinto supports the process
Sprinto's compliance automation platform supports the organisation of compliance work, evidence collection and ongoing monitoring. We are using it to support our readiness evaluation and bring structure to the process.
Across these engagements, Sprinto is helping us implement the ISO 27001 management system and assess readiness for SOC 2, GDPR and HIPAA. Having that work organised helps teams see what needs attention and maintain the documentation behind their decisions.
The responsibility for our policies, controls and follow-through remains with us. Independent assessment remains separate from that support. The ISO 27001 engagement provides for an external audit and certification process, while SOC 2 provides for an independent audit. The GDPR and HIPAA work addresses the relevant privacy practices and planned agreements.
What this means for our customers
The purpose of this work is to strengthen the practices behind the services our customers rely on and make those practices easier to explain and review.
The planned independent assessments and privacy agreements support different parts of that relationship, from supplier due diligence to clearer responsibilities for handling data. The requirements still need to reflect each organisation, the information involved and the way a system will be used. An audit report, certification or signed agreement supports that work, but cannot establish on its own that every customer configuration meets every applicable obligation.
Our role is to translate agreed requirements into practical HubSpot architecture, permissions, integrations and operational processes. Our own compliance programme supports the governance behind that delivery.
You can read more about our current approach on our data security page.
Continuing the work with Sprinto
Our next steps are to continue the ISO 27001 implementation and progress the SOC 2, GDPR and HIPAA readiness assessments. This includes preparing for the independent audits and putting the relevant privacy practices and agreements in place through the programme.
We will share updates as the programme develops, with clear explanations of what each milestone means. A huge thanks to the team at Sprinto for helping us put this into motion.
We look forward to continuing the work together and keeping our customers informed as we progress.